The Ultimate Guide to Phishing
A curated Australian edition of TechDay news, analysis, interviews, reviews, job moves, and related resources for Phishing.
What to know about Phishing
Phishing, a pervasive form of cybercrime, continues to evolve in sophistication and scale, posing significant risks to individuals and organisations worldwide. This tag gathers extensive insights into phishing tactics, including traditional email scams, spear-phishing, SMS phishing (smishing), and emerging AI-assisted attacks that exploit human vulnerabilities and trusted brand impersonations.
Recent stories highlight the increasing frequency and complexity of phishing attacks, such as operations targeting specific sectors like finance, industrial engineering, and healthcare. Reports reveal how cybercriminal groups adapt by leveraging multi-factor authentication exploits, brandjacking, and sophisticated social engineering to compromise credentials and infiltrate networks.
Readers exploring this tag will gain valuable understanding of how phishing attacks are conducted, who the most vulnerable targets are—from individual contributors to C-suite executives—and what measures organisations and individuals can take to mitigate risks. The tag also delves into cybersecurity solutions, training programs, and industry collaborations designed to bolster phishing resistance, emphasizing the critical role of combining technology, awareness, and proactive defense to combat this ever-changing threat landscape.
Australian Phishing News
Regional stories with direct local relevance
Data theft overtakes encryption in cyber intrusions
Stolen information is now the main pressure point in cyber intrusions, with exfiltration appearing in 83 per cent of cases investigated in the third quarter.
AI cuts entry-level cyber jobs in Australian firms
A Barracuda survey suggests junior cyber careers are thinning as 45% of Australian organisations swap or drop entry-level roles for AI.
Australia 11th in Microsoft cyber report as phishing rises
Phishing now accounts for nearly a quarter of observed intrusions, while Australia slipped to 11th in Microsoft's latest global cyber rankings.
Passkeys offer greater security as AI lowers phishing barrier
AI-generated phishing is making employee vigilance less reliable, pushing organisations towards passkeys and phishing-resistant multi-factor authentication.
Australian firms lag on passkeys as AI phishing rises
Australian firms remain exposed as 43% reported AI-driven phishing attacks in the past year, while many staff still log in with passwords.
Australian firms lag on AI cyber risk understanding
Only 20% of Australian organisations say they fully understand AI cyber risks, leaving boards exposed as phishing and deepfakes grow more credible.
Analyst Insights
Research and market analysis connected to Phishing
Bitdefender partners Digimune to sell consumer security

Financial firms face rising AI cyber risk, survey says
Financial services breach risk rises as AI adoption surges
AI is already running inside the enterprise. Is Australia ready?

KnowBe4 wins Frost & Sullivan email security award
Featured News
Palo Alto Networks: AI hunting vulnerability in legacy systems
Critical infrastructure operators are being urged to merge IT and OT security as AI speeds up attacks on ageing industrial systems.
Passkeys offer greater security as AI lowers phishing barrier
AI-generated phishing is making employee vigilance less reliable, pushing organisations towards passkeys and phishing-resistant multi-factor authentication.
AI attacks demand operational change in the post Mythos era
Only 5% of Australian companies are ready for AI-driven attacks, leaving most exposed as threat actors move at machine speed.
AI gives criminals speed boost, but basic security failures persist
Australian firms still face email compromise and poor security hygiene, even as AI helps criminals move faster and hide harder.
Mimecast CEO: Agentic AI threat novel but not entirely new
Hidden AI risks are already widespread in workplaces, with Mimecast saying users are driving shadow tools and most exposure still starts with people.
AI models expose new attack surfaces through misconfiguration
Misconfigured models are giving attackers a fresh route into cloud systems, raising the risk of data theft and service compromise.
CrowdStrike report: AI is rewriting rules of cybersecurity
Organisations now have just 48 hours to patch most flaws, as AI helps attackers weaponise vulnerabilities far faster than before.
Expert Columns
Cyber security now starts at the job interview
SOCtoberfest: The four habits that stop most attacks - passwords, MFA, phishing and patching
SOCtoberfest Kickoff: The 7 Deadly Sins of Cybersecurity Meet CISA's Core Steps
Why AI-Written Phishing Is Outpacing the Native Filters Built to Stop It

Mathspace Breach Exposes 1 Million Students, Parents, and Teachers
Weaponizing trust: How AI and social engineering bypass personal security boundaries
Fighting fraud at scale: Why entitlement servers are becoming central to telecoms security
No one's just a number: the finance-team blind spot behind Australia's rising payment scams
When AI accelerates the threat, identity governance cannot afford to stand still
AI agents are moving fast. Here's what Australians should understand before using them
Interviews
Interviews and video coverage from the network
Palo Alto Networks: AI hunting vulnerability in legacy systems
Passkeys offer greater security as AI lowers phishing barrier
AI attacks demand operational change in the post Mythos era
AI gives criminals speed boost, but basic security failures persist
Mimecast CEO: Agentic AI threat novel but not entirely new
Recent Phishing News
Keeper adds on-device AI phishing warnings to browser
The browser extension now flags look-alike login pages locally, helping users block credential theft before passwords are submitted.
Acronis warns awareness gap leaves users open to hacks
Basic cyber hygiene is still patchy, with 35% of people not backing up data regularly as phishing and AI-driven attacks keep rising.
Scams overtake phishing as attacks grow shorter-lived
Scam detections nearly doubled to 6.4 million as criminals shifted to faster-moving fraud that can evade takedowns and hit consumers directly.
Google uncovers brief AOMEI supply chain malware attack
Systems that polled AOMEI's update servers at the wrong moment could have pulled malicious files in the brief April-to-July tampering window.
Hotejka scam network uses free hosting to target users
Researchers say the scheme has run since 2017, exposing users to fake Microsoft alerts and remote access theft through legitimate hosting tools.
CrowdStrike finds AI agents running autonomous cyberattacks
CrowdStrike found four threat actors using AI agents to automate cyberattacks, compromising healthcare, government and private-sector organisations.
Proofpoint joins Microsoft ICES in Defender portal
Microsoft 365 customers can now review Proofpoint email threat alerts inside Defender, cutting the need to switch between security tools.
Global cyber attacks jump 48% as phishing rises
Organisations faced 2,803 attacks a week on average in September as phishing and ransomware added to pressure on corporate and public sector systems.
Jev AI lookalike domains surge after launch, UpGuard warns
Users could have prompts, files and API keys stolen as 167 lookalike domains linked to Jev were registered within 13 days of launch.
ThreatDown ties criminal AI storefronts to OpenRouter
The discovery suggests takedowns may be fleeting, as criminals can quickly rebuild AI storefronts using the same rented routing layer and models.
Secure.com says ransomware budgets should fix basics first
Most attacks still start with weak credentials, unpatched systems or phishing, so the firm says budgets should shore up basics before AI fears.
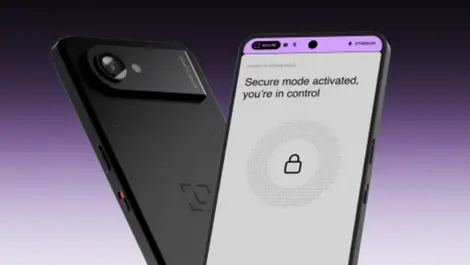
Ledger launches Atom security device for AI & crypto
It is aimed at people approving payments, identities and AI tasks on mobiles, with hardware controls designed to block spyware and mistakes.
Australia targeted in massive phishing network takedown
Financial, healthcare and public-sector organisations face less immediate pressure after a disruption effort hit a phishing network sending more than 1 billion malicious messages.
Identity-led intrusions drive cyber extortion tactics
Attackers are exploiting trusted identities and collaboration tools to steal data and extort victims, leaving defenders with only brief windows to react.
Memcyco updates PoSA to spot attacker devices earlier
Fraud teams can now flag suspicious devices before login, as PoSA v1.11 adds real-time risk scores to help stop account takeovers earlier.
Check Point warns of 48% rise in cyber attacks worldwide
Sensitive data exposure through workplace AI is compounding a 48% annual rise in attacks, with organisations hit by 2,803 per week in September.
Dashlane expands SIEM integrations with browser telemetry
The move aims to close a browser visibility gap, giving security teams earlier warning of risky logins and phishing without another console.
China-linked TA419 targets US AI policy experts in phishing
Researchers say the phishing campaign could expose sensitive thinking on AI regulation, export controls and supply chains in Washington.
Rapid7 launches intelligence platform to outpace hackers
The new system aims to help security teams spot attacks sooner as AI-driven exploitation narrows the window between flaw disclosure and abuse.
Microsoft warns AI is deepening cyber threat links
Threats are now spanning identities, cloud and software supply chains, with AI speeding attacks and complicating defence, Microsoft says.