

Australia tops IoT & OT cyberattack list, says report
Tue, 13th Oct 2026 (Today)
Australia was the most targeted country for IoT and OT cyberattacks in Nozomi Networks Labs' latest threat intelligence report, up from third place in the previous edition.
The research tracked malicious activity across operational technology, internet of things and critical infrastructure environments over three months. It found that Australian organisations generated the highest number of alerts per organisation among all countries monitored.
The UK ranked second, while France moved into third place, replacing Germany. According to Nozomi, the shift reflects sustained attacker focus on Australian infrastructure as cyber risks continue to affect both industrial systems and connected devices.
Sector exposure
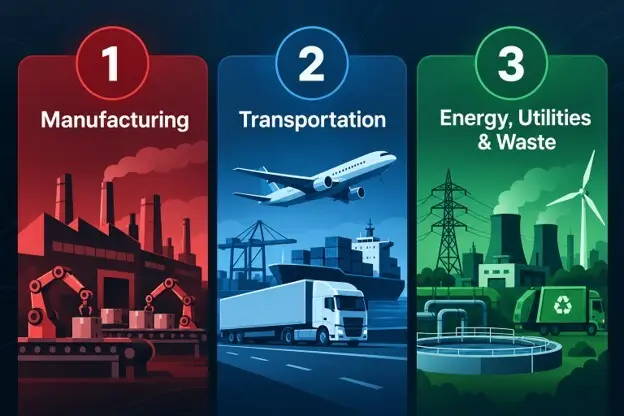
Manufacturing was the most targeted industry, overtaking transportation, which had led in the second half of 2025. Energy, Utilities and Waste rose to third place, replacing the government sector.
These sectors share characteristics that can increase their exposure to cyber intrusion. They rely heavily on interconnected OT and IoT systems, often use legacy equipment that is difficult to patch, and can face significant disruption from even short outages.
That profile can make them attractive to attackers seeking operational disruption or leverage for extortion. In utilities and other public-facing services, a successful compromise can also have immediate visible consequences.
Threat actors
Nozomi also examined activity attributed to threat actors. Scattered Spider was the most prolific group in the dataset, accounting for 48.0% of actor-attributed alerts.
The group, which the report linked to the US and UK, is known for social engineering attacks. UNC4536, described as an unknown but apparently Russian-speaking actor, ranked second with 20.8% of attributed alerts.
RomCom, which Nozomi linked to Russia, ranked third with 12.53%, followed by UNC5636 with 11.4%. APT29, also linked to Russia, accounted for 2.98%, completing the top five.
Taken together, the Russian-linked or Russian-speaking actors in the report accounted for more than a third of attributed alerts. The findings point to a threat environment shaped by both financially motivated groups and geopolitically linked actors.
Scattered Spider's prominence also underscores the role of social engineering in attacks on industrial and connected environments. Rather than relying solely on software flaws, some attackers continue to target people and identity processes to gain access.
Common methods
Despite the range of actors involved, the report found that their techniques were broadly consistent. Default and weak credentials, discovery scanning and denial-of-service techniques featured prominently across multiple attack groups.
The repeated use of these basic methods suggests that many connected industrial and IoT environments remain exposed through longstanding weaknesses rather than highly specialised intrusion techniques. Weak passwords and internet-exposed assets continue to provide attackers with an entry point.
The report also noted faster vulnerability discovery and exploitation cycles, alongside the continued evolution of botnets capable of generating large volumes of opportunistic traffic. That combination can increase pressure on organisations with large numbers of connected devices spread across IT and OT networks.
Operational risk
For industrial operators, the issue is not only data loss or system compromise but also business interruption. In sectors such as manufacturing, transport and utilities, service outages can halt production, disrupt logistics or affect essential services.
Nozomi said organisations in these industries should align security spending with operational risk, improve visibility into critical processes, separate IT and OT networks, and maintain response plans designed to limit the effects of a successful intrusion.
It also urged defenders to focus on the behaviours and indicators left by threat actors and to keep detection logic updated as new intelligence emerges.
Overall, the report concluded that the threat landscape remains shaped by familiar weaknesses, with default credentials, exposed assets and social engineering still central to attacks on connected industrial environments.